ISO 9001 governs quality management, the consistency of products, services, and customer outcomes. ISO 45001 governs occupational health and safety, the prevention of workplace injury and ill health. Choose ISO 9001 when customer satisfaction and process reliability are the dominant business risk, choose ISO 45001 when worker safety carries the greater exposure, and integrate both when your organization faces material risk on each front simultaneously.
TL;DR:
- ISO 9001 is typically prioritized for construction firms with material customer satisfaction risks, such as quality failures or repeated rework, especially when tender scoring favors it.
- ISO 45001 addresses safety risks like site incidents and near misses and is often required by insurers or principal contractors for high-hazard projects.
- Both standards follow the Annex SL structure, allowing for integrated management systems, but operational controls and performance indicators differ significantly between quality and safety scopes.
- Certification often takes several months, involving gap analysis, leadership commitment, documentation, training, internal audits, and external certification, with small organizations facing longer timelines.
- Targeted site-level support, including templates, training, and audit preparation, is essential for successful certification and improved daily safety and quality practices.
Table of Contents
- ISO 9001 vs ISO 45001: A Side-by-Side Comparison
- Where the Clauses Overlap and Where They Diverge
- How Do You Choose Between ISO 9001 and ISO 45001?
- From Gap Analysis to Certification: The Implementation Path
- What Does ISO Implementation Look Like in Construction?
- The Practical Verdict on ISO 9001 vs 45001
- Get Hands-On Support for ISO 9001 or ISO 45001 Certification
- Sources
- FAQ
ISO 9001 vs ISO 45001: A Side-by-Side Comparison
The two standards solve different problems for different stakeholders, and confusing them is the most common mistake we see among construction firms preparing their first certification bid. ISO 9001 exists to make product and service delivery predictable and to demonstrate a credible commitment to customer satisfaction. ISO 45001 exists to prevent work-related injury and ill health, and it replaced OHSAS 18001 as the recognized global benchmark for OH&S management.
The affected parties differ sharply. ISO 9001 is answerable primarily to customers, buyers, and contractual counterparties who care whether the concrete pour, the fabricated steel, or the delivered service meets specification every time. ISO 45001 is answerable to workers, contractors, subcontractors, and site visitors, plus the regulators who enforce statutory OH&S obligations regardless of whether a company holds any certificate at all.
Both deliver distinct, measurable business value:
- ISO 9001 reduces rework, cuts customer complaints, and strengthens tender submissions where quality assurance is a prequalification requirement.
- ISO 45001 lowers incident rates, builds a genuine safety culture through leadership commitment and worker participation, and can reduce insurance premiums over time.
- Combined, the two standards cut duplicated administration because both share Annex SL’s audit and documentation architecture, meaning one internal audit program can often cover both scopes.
- Neither certificate is legally compulsory in most jurisdictions, though contract terms, client mandates, or sector regulation frequently make certification a practical necessity for winning work.
For a general contractor bidding on public infrastructure work, ISO 9001 often arrives first because tender scoring rewards it. For a demolition or high-rise formwork specialist, ISO 45001 often takes priority because the hazard profile is severe enough that insurers and principal contractors demand it outright.
Where the Clauses Overlap and Where They Diverge
Both standards follow the Annex SL high-level structure: context of the organization, leadership, planning, support, operation, performance evaluation, and improvement. That shared skeleton is why so many organizations run both under one integrated management system rather than two parallel bureaucracies.
Reuse and divergence follow a predictable pattern:
- Document control, internal audit programs, and management review are structurally almost identical across both standards and can typically be operated as a single unified process.
- Competence, awareness, and communication requirements overlap heavily, though ISO 45001 adds explicit emphasis on worker participation and consultation that ISO 9001 does not require.
- Operational planning and control diverges technically: ISO 9001 focuses on product and service acceptance criteria, while ISO 45001 focuses on hazard identification, risk assessment, and the hierarchy of hazard controls.
- Performance evaluation shares the audit cycle but tracks different indicators: nonconformity and customer complaint trends for quality, incident and near-miss data for safety.
A clause-level matrix makes this concrete: a single management review meeting can cover both quality and safety KPIs, but the hazard register that feeds ISO 45001’s operational controls has no equivalent in ISO 9001’s clause structure.
Pro Tip: Run one combined internal audit calendar but keep two separate evidence folders. Auditors want to see that hazard controls and product acceptance records were assessed on their own technical merits, not folded into a generic checklist.
How Do You Choose Between ISO 9001 and ISO 45001?
Start with the question your business actually faces, not the standard that sounds more prestigious. Ask these four things before committing resources:
- What is your material risk? Frequent product defects or customer disputes point toward ISO 9001; a history of site incidents or near misses points toward ISO 45001.
- What do your customers or principal contractors require? Many tender documents in construction now specify one or both certifications as a prequalification gate.
- What does your regulator expect? Statutory OH&S duties exist whether or not you certify, so certification often follows from an existing compliance gap rather than creating a new obligation.
- What does your gap analysis show? Pull incident history, customer complaint logs, and current process maturity before deciding, since material risk usually settles the argument faster than internal debate does.
If both risks are genuinely material, start implementation with whichever one addresses your most urgent exposure, then layer in the second standard using shared governance rather than starting from zero twice.
From Gap Analysis to Certification: The Implementation Path
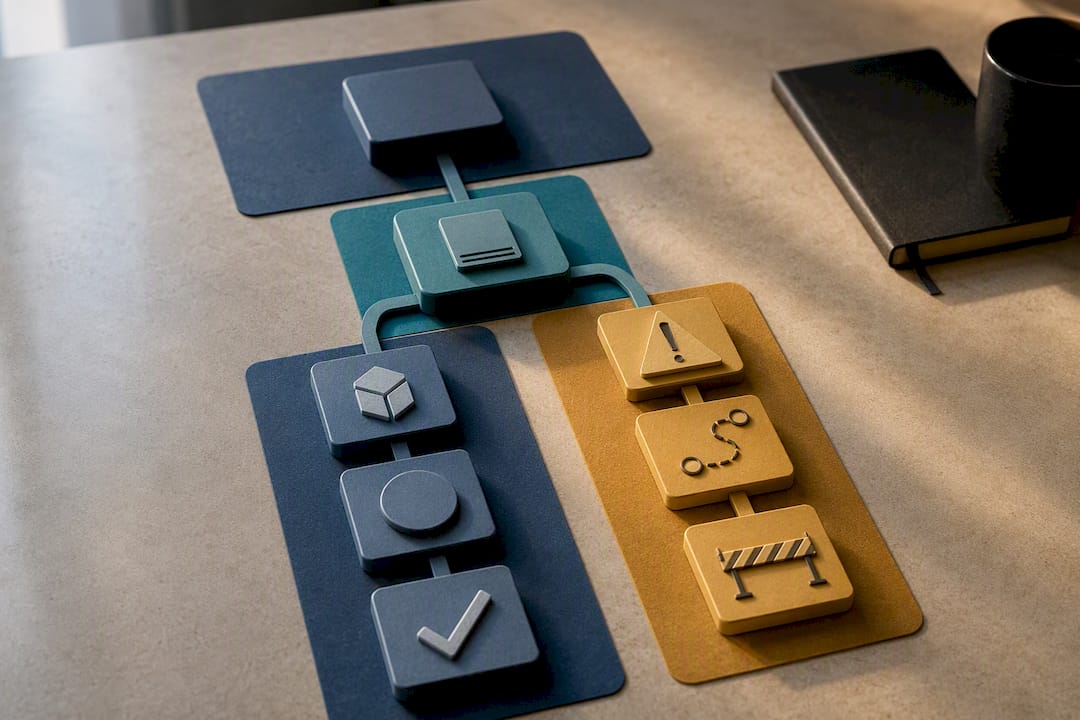
Certification is not a single event. It is a multi-year cycle, and organizations that treat it as a one-off audit tend to lose their certificate within the first surveillance cycle. A realistic implementation path runs through six phases:
- Gap analysis against the target standard’s clauses, benchmarked against current documentation and site practice.
- Leadership commitment, formalized through a documented policy and named management representative.
- Documentation build, covering the management system manual, procedures, and the technical evidence unique to each standard.
- Training and awareness, extended to workers, supervisors, and subcontractors where ISO 45001 is in scope.
- Internal audit, testing the system before an external body sees it.
- Certification audit, followed by surveillance audits across a three-year recertification cycle.
Timeline reality check: implementation for small and mid-sized organizations typically runs several months, depending heavily on how mature existing documentation already is and how much dedicated staff time leadership commits to the project.
The most common pitfall in integration is collapsing technical evidence into one generic checklist. Governance processes such as management review and document control combine cleanly; hazard registers, risk assessments, and product acceptance criteria do not, and trying to force them into a single form usually fails the certification audit. An integrated management system works best when governance is unified and technical evidence stays discipline-specific.
What Does ISO Implementation Look Like in Construction?
Construction firms rarely need a textbook explanation of Annex SL. They need someone to translate it into site-level practice. A typical consultancy engagement covers a gap analysis against current site documentation, ready-to-use templates for hazard registers and quality records, worker and supervisor training, and hands-on audit readiness support before the certification body arrives.
The realistic payoff is a stronger tender submission, fewer nonconformities at audit, and a measurable shift in how seriously workers treat safety procedures day to day, not a guaranteed outcome, but a consistent pattern across firms that commit to the process. Before engaging any consultant, ask for references from comparable contractors, a sample project timeline, and evidence of past certification outcomes.
- Gap analysis mapped to your current site documentation
- Templates for hazard registers, quality records, and audit trails
- Worker, supervisor, and management training aligned to the target standard
- Audit readiness support in the weeks before the certification body visits
The Practical Verdict on ISO 9001 vs 45001
Pick the standard tied to your actual material risk, not the one with better brand recognition. When both quality and safety risks are real, integrate the governance layer but never merge the hazard register with the quality file. The single best next move for most readers is a short gap analysis this quarter, backed by a written commitment from senior leadership.
— Aman
Get Hands-On Support for ISO 9001 or ISO 45001 Certification
Reading about clause mapping is one thing. Building the documentation, training your crews, and passing the certification audit is another. Consultants typically have extensive experience guiding construction firms through both processes, building hazard registers, quality records, and audit evidence specific to site conditions rather than using a copy-paste framework.
Whether you need ISO 9001 to strengthen tender submissions or ISO 45001 to address a genuine safety exposure, our ISO Certification service starts with a gap analysis against your current documentation, followed by tailored training and audit readiness support through to the certification audit itself. For firms weighing an integrated approach, our broader consultancy services cover both quality and OH&S scopes under one engagement. Reach out to scope your gap analysis and get a realistic timeline for your certification path.
Sources
- ISO 9001 explained
- ISO 45001:2018 vs ISO 9001:2015 matrix (Advisera)
- 5 things to know about the new SS ISO 45001
FAQ
Is ISO 9001 Changing in 2026?
A draft revision, ISO/FDIS 9001:2026, is in development, but organizations should verify final requirements directly on ISO’s official pages rather than treating draft content as settled.
What Is the Difference Between ISO 9001, ISO 14001, and ISO 45001?
ISO 9001 covers quality management, ISO 14001 covers environmental management, and ISO 45001 covers occupational health and safety. All three share the Annex SL structure, which is why many organizations run them as one integrated system. For a closer look at environmental and safety overlap specifically, see how ISO 14001 compares to ISO 45001.
What Are the Core Elements of ISO 45001?
ISO 45001 is built around leadership commitment, worker participation, hazard identification and risk assessment, operational controls, incident investigation, and continual performance evaluation, all organized under the Annex SL framework.
Is ISO 45001 Certification Mandatory?
No. Certification is voluntary and performed by independent certification bodies, but statutory OH&S obligations apply to employers regardless of certification status. Many principal contractors and tenders still require it as a practical condition of doing business, and services like ISO 45001 certification consulting exist specifically to help firms meet that bar.
