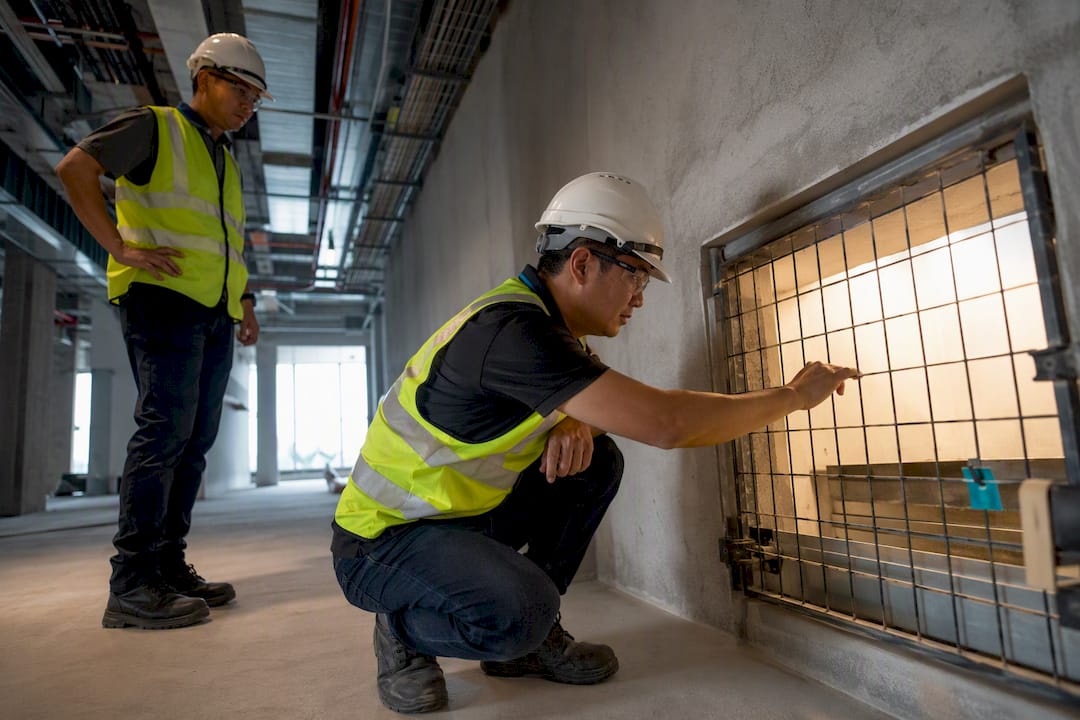
If your construction contract sum is S$30 million or more, you must schedule a ConSASS audit at a minimum frequency of twice a year, engage an MOM-approved WSH auditor from a SAC-accredited auditing organisation, and submit the completed audit checklist, scorecard, and final report through MOM WSH eServices using Singpass authentication. Missing any one of these elements exposes the project to regulatory scrutiny.
TL;DR:
- Contractors with projects exceeding S$30 million must schedule ConSASS audits twice annually, involving SAC-accredited auditors and submitting detailed reports through MOM WSH eServices.
- The mandatory audit scope covers all sites crossing the S$30 million threshold, regardless of project length, with the occupier responsible for compliance and submission deadlines.
- The ConSASS checklist features over 200 questions aligned with ISO 45001, assessed across three bands, with each band requiring around 70% passing score before proceeding.
- Only auditors from MOM-recognized SAC CT-17 accredited organisations can perform ConSASS audits, and verification of accreditation before engagement is essential.
- Preparation should include early site familiarization, assembling representative interview samples, and timely documentation updates, as follow-up audits are narrower and must fit within existing schedules.
Table of Contents
- Scope and timing: who is in-scope and the legal timeframe
- ConSASS checklist, banding and verification methods
- Auditor and auditing organisation requirements
- Submission and documentation: what to upload and how
- Practical audit preparation: sampling, interviews and pitfalls
- How MOSAIC supports ConSASS readiness
- Detailed timeline for the ConSASS audit process
- Consequences of non-compliance or failing the audit
- Handling repeat audits after an initial failure
- Practitioner perspective: ConSASS as continuous improvement
- Get ConSASS-ready with MOSAIC’s audit and compliance support
- Official downloads and reference links
- Sources
- FAQ
Scope and timing: who is in-scope and the legal timeframe
The contract sum threshold is the single determining factor for mandatory ConSASS coverage. Any worksite where the contract sum reaches S$30 million or more falls under the mandatory audit regime, and the statutory duty rests with the occupier of the worksite, typically the main contractor or the party in physical control of operations, to appoint an approved external auditing organisation. This obligation is independent of project duration; a multi-year development does not get a single pass and a clean exit.
The minimum frequency is fixed at once every six months for the life of the project once the threshold is crossed. For a project spanning several years, that means the occupier plans for a recurring audit calendar from groundbreaking through to completion, not a one-off compliance event scheduled around a milestone.
The ConSASS framework, formalized through the Workplace Safety and Health Council and administered by the Ministry of Manpower, has evolved since its earlier iterations, with a significant revision taking effect in 2020 that reshaped the checklist structure. For site managers, the practical takeaway sits in three points:
- Confirm your contract sum against the S$30 million threshold before the project starts, not after MOM flags a gap.
- Build the six-monthly audit cycle into the master project schedule alongside other statutory milestones.
- Assign the occupier’s compliance owner clearly, since the appointment duty and submission responsibility sit with that role.
ConSASS checklist, banding and verification methods
The ConSASS checklist is structured around roughly over 200 questions across 20 elements aligned to the ISO 45001 Plan-Do-Check-Act model, replacing the older format with a leaner, implementation-focused structure. This alignment matters because it means a site already working toward ISO 45001 certification is, in effect, building much of its ConSASS evidence base at the same time.

Each element is assessed across three bands. Band I typically cover planning and system documentation, Band II covers implementation, and Band III covers deeper performance verification. Auditors apply a pass threshold of around 70% at each band, and if an element fails to clear Bands I or II, auditors are not required to proceed to Band III for that element. This rule keeps the audit efficient by concentrating on-site time where evidence is actually achievable rather than chasing scores on a foundation that has already failed.
Verification runs through three methods, each suited to a different kind of evidence:
- Document review (DR), used to confirm policies, procedures, and records exist and are current.
- Interview (IP), used to test whether workers and supervisors understand and apply the system in practice.
- Physical inspection (PI), used to confirm conditions on the ground match what the paperwork and interviews claim.
204 questions span the full ConSASS checklist, and the 2020 revision reduced the total count while sharpening the focus on implementation evidence rather than paperwork alone, a shift that changes how site teams should prepare.
Auditor and auditing organisation requirements
Not every safety consultant can conduct a ConSASS audit. The auditing organisation itself must hold SAC CT-17 accreditation, the specific accreditation scheme under the Singapore Accreditation Council that governs WSH auditing bodies, and each individual auditor must appear on that organisation’s SAC AO Schedule before they are recognized to perform statutory audits.
To verify legitimacy before signing an engagement, work through these steps:
- Check that the auditing organisation is listed as SAC-accredited under the CT-17 scheme, not merely SAC-accredited in general.
- Confirm the named auditor appears on that organisation’s current AO Schedule, since accreditation covers the organisation and named individuals separately.
- Confirm the organisation has completed MOM registration as a recognized WSH auditing organisation, which requires submitting accreditation documents and auditor credentials to MOM directly.
- Confirm the audit team assigned to your site meets the minimum audit team of two auditors, a requirement that supports independent cross-checking of findings.
Pro Tip: Ask the auditing organisation for their current SAC AO Schedule listing in writing before the audit date, since accreditation status can change between engagements.
Submission and documentation: what to upload and how
Three documents form the core of every ConSASS submission: the completed checklist, the scorecard, and the final audit report. These must be uploaded through MOM WSH eServices, and the platform requires Singpass authentication from an authorized company representative, meaning the person submitting must be empowered to act for the occupier on record.
Before the submission window opens, gather the following:
- The completed ConSASS checklist showing element-by-element scoring across all applicable bands.
- The scorecard summarizing performance by element, which management typically uses to prioritize corrective action.
- The final audit report from the SAC-accredited organisation, signed by the lead auditor.
Once submitted, the same eServices portal allows the occupier to check submission status and retrieve past reports, which is useful when preparing for a subsequent audit cycle or responding to an MOM query. Organisations still working through the transition from the older four-band format should apply the official conversion matrix when submitting, since the portal’s historical structure has not yet been fully updated to match the current three-band system.
Practical audit preparation: sampling, interviews and pitfalls
Sampling rules determine how much evidence auditors actually check. For document review and interviews, the working guidance is a minimum sample of three, with at least two of three needing to meet the intent for that item to pass.
Follow these steps when preparing for the audit window:
- Assemble a representative interview pool of at least 12 workers and supervisors across trades and shifts, since a narrow sample skews results toward whichever team happens to be available on audit day.
- Walk the site yourself before the audit using the checklist as a guide, since a familiarization tour is standard practice in the auditor’s own methodology and catches gaps early.
- Expect the audit to open and close with formal meetings, with on-site man-days scaled to project size, so block out enough calendar time rather than compressing the visit.
Pro Tip: The most common fail point is not missing paperwork, it is workers on the ground who cannot explain a procedure that looks complete on paper, so rehearse interview readiness as seriously as document readiness. Further preparation guidance, including how to align evidence gathering with day-to-day site operations, is covered in MOSAIC’s guide on protecting people and securing projects.
How MOSAIC supports ConSASS readiness
Construction companies preparing for ConSASS audits can engage experienced QES consultancy services for the construction sector. Typical services include pre-audit gap analysis against the current checklist, alignment of existing documentation with safety frameworks, on-site support during the audit, and assistance preparing files for MOM WSH eServices submission.
The practical benefit of this kind of support shows up before the auditor ever arrives: gaps in documentation or interview readiness surface early enough to fix, rather than during the audit when the clock is already running. Readers can review the operational case for regular audits in more detail on MOSAIC’s page on the benefits of conducting regular ConSASS audits.
Detailed timeline for the ConSASS audit process
A ConSASS audit cycle typically runs across four phases, and site managers who treat these as sequential rather than compressed tend to avoid last-minute scrambles.
Preparation begins weeks before the audit date. This is when the occupier confirms the auditing organisation’s accreditation, schedules the audit team, and runs an internal gap check against the checklist elements.
Pre-audit alignment follows, where documentation is updated, toolbox talks and permits are brought current, and supervisors brief workers likely to be interviewed. This phase is where most of the real compliance work happens, since the audit itself is largely a verification exercise rather than a discovery process.
The audit visit opens with a formal meeting, moves through a site familiarization tour, then proceeds through document review, interviews, and physical inspection in whatever order the audit team finds efficient, and closes with a debrief meeting where preliminary findings are shared.
Reporting and submission follows the visit. The auditing organisation compiles the checklist, scorecard, and final report, and the occupier’s authorized representative submits these through MOM WSH eServices using Singpass. Building buffer time into this phase matters, since report compilation and internal sign-off can take longer than the audit visit itself.
Consequences of non-compliance or failing the audit
A worksite that skips a scheduled ConSASS audit, or fails to submit the required documents through MOM WSH eServices, is out of compliance with a statutory safety management system requirement, and MOM retains enforcement powers over worksites that fall short of workplace safety and health obligations. The specific penalty structure applied in any given case depends on MOM’s own assessment and is not something a general guide should predict.
Beyond formal enforcement, a failed or overdue audit carries operational costs that site managers often underestimate. A poor scorecard signals systemic weakness in the safety management system, which tends to correlate with a higher rate of incidents and near-misses on-site, the exact outcome ConSASS exists to prevent. Developers, main contractors further up the chain, and tender evaluators increasingly ask to see recent ConSASS results as part of due diligence, so a weak or missing record can affect a firm’s ability to win future work, not just its standing on the current project.
The most immediate practical consequence, though, is simply lost time. An occupier that fails an audit does not get to walk away. It has to remediate the failed elements and go through a follow-up process, which pulls management attention away from the project itself at exactly the point when the project needs it most.

Handling repeat audits after an initial failure
The auditing organisation’s final report should identify exactly which elements and bands fell short, giving the occupier a specific punch list rather than a vague instruction to try harder.
The practical sequence looks like this: review the scorecard element by element, assign corrective actions to the responsible supervisors or subcontractors, close out those actions with documented evidence, and then schedule a follow-up audit on the failed elements specifically. Because Band III is skipped when Bands I or II fail, a follow-up audit often has a narrower scope than the original visit, since the team already knows exactly where the gaps were.
One nuance worth flagging: the six-monthly audit cycle does not pause because of a failed result. If the next scheduled audit falls due before remediation is complete, the occupier still needs to plan for it, which means remediation timelines should be set against the existing audit calendar rather than an open-ended internal deadline. Firms managing multiple sites often find it easier to treat every scorecard as a live action list rather than a filed report, updating it continuously between audit cycles instead of rediscovering the same gaps every six months.
Practitioner perspective: ConSASS as continuous improvement
Treating ConSASS as a compliance hurdle rather than a management tool wastes the exercise. The scorecard is a prioritization tool: use it to rank which elements need attention before the next cycle, not just to file a pass. Aligning ConSASS evidence with ISO 45001 documentation and BizSAFE processes cuts duplicated work substantially. Verify auditor accreditation early, and submit promptly, since delay compounds risk without adding value.
— Aman
Get ConSASS-ready with MOSAIC’s audit and compliance support
Preparing for a ConSASS audit while running a live construction site is a demanding balance, and getting the checklist, scorecard, and final report submission wrong costs time you do not have. MOSAIC’s ConSASS service is built around exactly this problem: a specialist team that handles gap analysis, documentation alignment, and on-site audit support so your project team can stay focused on construction rather than compliance paperwork.
Engaging MOSAIC typically covers:
- A pre-audit gap analysis against the current checklist elements and bands.
- Documentation and evidence alignment across ConSASS, BizSAFE, and ISO certification requirements.
- On-site support during the audit visit and assistance preparing files for MOM WSH eServices submission.
If your contract sum has crossed S$30 million or your next six-monthly window is approaching, get in touch with MOSAIC’s ConSASS team to schedule a readiness check before your audit date is locked in.
Official downloads and reference links
- MOM ConSASS user guide (PDF)
- MOM eServices: submit a ConSASS audit
- SAC CT-17 auditing organisation registration
- WSH Council ConSASS 2020 briefing
For readers managing risk registers alongside audit findings, this guide on building a construction risk register quickly offers a useful complementary framework.
Sources
- Construction Safety Audit Scoring System (ConSASS) user guide
- Submit a ConSASS audit – MOM
- Apply for WSH auditing organisation – MOM
- New ConSASS checklist scorecard interview sheets and user guide now available for download – WSH Council (TAL)
FAQ
What are the requirements for a ConSASS audit?
A worksite with a contract sum of S$30 million or more must engage a SAC-accredited auditing organisation to audit its safety management system at a minimum frequency of twice a year. The occupier must then submit the completed audit checklist, scorecard, and final report through MOM WSH eServices using Singpass authentication.
What are the requirements for an audit in Singapore?
Requirements vary by audit type, but for statutory workplace safety audits like ConSASS, the core requirements are an MOM-approved auditor from a SAC CT-17 accredited organisation, adherence to the checklist’s banding and sampling rules, and submission of results through the official MOM channel. General safety audits outside the mandatory ConSASS threshold follow similar documentation and verification principles but without the fixed six-monthly submission duty.
How often should a ConSASS audit be conducted?
For worksites meeting the S$30 million contract sum threshold, ConSASS audits are required at a minimum frequency of twice a year for the duration of the project. This cycle continues regardless of whether a previous audit passed or required remediation.
What are the 5 standards of internal audit?
Definitions of internal audit standards vary by framework and are not specific to ConSASS. For workplace safety and health audits in Singapore, the relevant reference point is the ConSASS checklist itself, which structures verification around document review, interviews, and physical inspection rather than a generic five-standard model.
Who can conduct a ConSASS audit?
Only MOM-approved WSH auditors from auditing organisations accredited under the SAC CT-17 scheme are authorized to conduct ConSASS audits. Each auditor must appear on the organisation’s current SAC AO Schedule before the engagement.