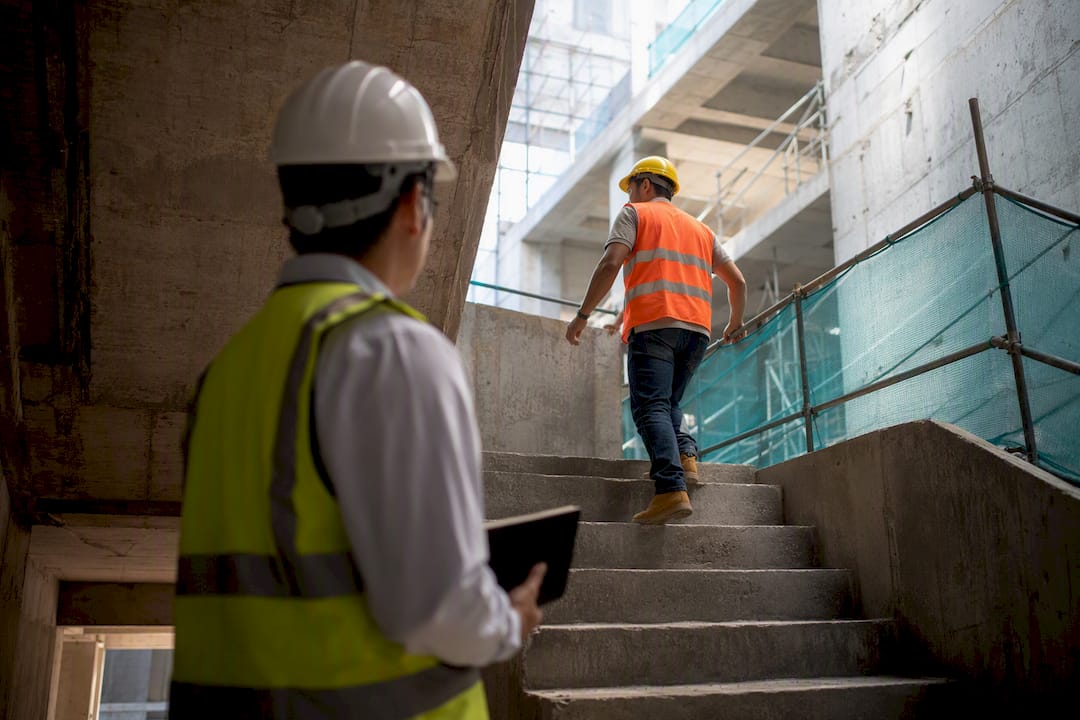
An internal WSH audit is a planned, evidence-based review of your safety and health management system against a chosen standard, not a paperwork inspection. Start by fixing two things before you walk the site: the scope of the review and the standard you will measure against, whether that is ConSASS, SS ISO 45001, or sector-specific MOM guidance. Certain worksites also fall under mandatory external audit triggers, so confirm your obligations before treating an internal review as sufficient on its own.
TL;DR:
- Internal WSH audits must be evidence-based, focus on system functionality, and verify that controls are in place and effective, not just check documentation.
- Auditors need proper training, independence, and documentation of qualification, with cross-department rotation and conflict-of-interest declarations to maintain credibility.
- The audit process involves careful planning, gathering evidence, site walk-throughs, worker interviews, scoring, and assigning corrective actions to ensure continuous improvement.
- Checklists must verify that policies are current, controls are physically present, and workers understand hazard management, with reference to key elements like leadership, risk controls, and incident review.
- For large projects over $30 million, ConSASS compliance is mandatory and uses a standardized scoring system, while smaller sites align internal audits with ISO 45001 standards for comparable rigor.
Table of Contents
- What Counts as an Internal WSH Audit (and What Doesn’t)
- Who Can Run the Audit Without Compromising It
- The Internal WSH Audit Process, Step by Step
- What Your Audit Checklist Should Actually Test
- Turning Findings Into a Report That Drives Change
- Where ConSASS and ISO 45001 Fit Into Your Audit
- Where Internal Audits Go Wrong on Real Sites
- Why We Treat Internal Audits as Foundational, Not Optional
- Get Expert Support for Your Next WSH Audit
- Where to Verify the Rules Yourself
- Sources
- FAQ
What Counts as an Internal WSH Audit (and What Doesn’t)
An internal WSH audit examines whether your Safety and Health Management System (SHMS) is functioning as designed. That is a different question from a workplace inspection, which checks physical conditions on a given day: guardrails in place, housekeeping standards met, fire extinguishers charged. An audit asks whether the system behind those conditions actually works: does your risk assessment process generate controls that get implemented, and does your training program produce workers who apply what they were taught?
MOM guidance sets statutory frequency bands for internal reviews based on project value. Worksites with a contract sum under $30 million must conduct internal reviews at least semi-annually, and this cadence is a floor, not a target. Companies serious about continual improvement often audit quarterly, particularly during high-risk phases like structural works or hot work campaigns.
A well-run audit does three things at once:
- Confirms the SHMS documentation reflects current site operations, not last year’s project.
- Verifies that documented controls are actually in use on the ground.
- Generates evidence management can act on, rather than a pass or fail stamp.
That last point separates a useful audit from a compliance exercise nobody reads twice.
Who Can Run the Audit Without Compromising It
Internal audits don’t require an external MOM-approved auditor in every case. MOM guidance allows staff who have completed recognized audit training, such as an ISO 45001 internal audit course, to conduct internal reviews and produce outcomes equivalent to a formal SHMS audit. The catch is independence: the person reviewing a department’s risk controls should not be the person who wrote them.
Practical measures that hold up under scrutiny:
- Rotate auditors across departments or projects so nobody audits their own work area.
- Document the selection criteria for your audit team, including training certificates and years of relevant experience.
- Keep a written conflict-of-interest declaration for each audit cycle, signed before the audit starts, not after a finding gets challenged.
High-exposure workplaces face a higher bar. MOM’s WHS+ consultation and audit programme requires gap analysis and, in some cases, third-party audits conducted by competent persons such as Registered Industrial Hygienists. If your operations involve chemical exposure, noise, or other health hazards beyond typical construction risk, check whether you fall into that category before assuming an internal review is enough.
Pro Tip: Assign a co-auditor with no reporting line to the site team. A second set of eyes with zero stake in the outcome catches soft findings that a lone internal auditor tends to wave through.
The Internal WSH Audit Process, Step by Step
An internal audit that skips straight to the checklist usually produces weak findings. The sequence matters as much as the content.
- Plan the scope. Decide which standard you’re auditing against, the time period your evidence will cover, and which elements get sampled this cycle. Pull the previous audit report and list every open finding, since closure verification is part of this audit, not a separate task.
- Prepare your evidence base. Gather policy documents, risk assessments, training records, permit-to-work logs, and incident reports for the sampled period. Build an interview list covering supervisors, workers, and at least one subcontractor representative. Draft a site sampling plan that names specific work areas, not “the site” as a whole.
- Execute in three layers. Review documents first to confirm they exist and are current. Walk the site to check whether documented controls are physically in place. Interview workers to test whether they understand and apply what the documents describe. This is the three-column test: documented, in use, and works, and skipping any column produces an audit that looks thorough but isn’t.
- Score each element. Apply a consistent rating (conforms, observation, minor nonconformance, major nonconformance) so results are comparable across audit cycles. Record the specific evidence that led to each score, not just the score itself.
- Assign corrective actions. Every finding gets an owner, a deadline, and a required piece of closure evidence, defined before the audit ends, not negotiated afterward.
Following structured construction audit steps keeps this workflow consistent across projects and audit cycles, which matters when you’re comparing trend data over a year of reviews.
What Your Audit Checklist Should Actually Test
A checklist that only asks “does the document exist” produces a false sense of security. Each core element needs a documented / in use / works verification, and the evidence you accept should differ by element.
- Policy and leadership. Look for a signed, current policy document, plus evidence of management review, such as minutes from a safety committee meeting where leadership actually engaged with findings.
- Hazard identification and risk control. Check risk assessments against the hierarchy of controls, then confirm on-site that the specified controls (barricades, local exhaust ventilation, permit conditions) are physically present, not just listed on paper.
- Competence and training. Pull training records, then interview two or three workers from the same training cohort to see whether they can explain the hazard controls relevant to their task.
- Contractor management and permits. Review contracts and permit-to-work records, and cross-check supervision logs to confirm someone actually signed off on conditions before work started, not after.
- Emergency preparedness and incident management. Check drill records against the required frequency, and review recent incident investigations for root-cause analysis rather than a one-line description of what happened.
- Monitoring and review. Look at KPI trends over time, and specifically verify that findings from the previous audit cycle are closed with evidence, not just marked complete in a spreadsheet.
A safety compliance checklist built around these six elements gives you a repeatable structure without forcing every audit into an identical template that ignores site-specific risk.
Turning Findings Into a Report That Drives Change

An audit report that just lists scores gets filed and forgotten. A report built for action includes an audit reference number, the defined scope, the standard used, the period of evidence sampled, and a written auditor independence statement confirming who ran the review and their relationship to the audited area.
Standardize your ratings so trends are visible across cycles:
- Conforms — evidence supports full implementation across all three columns.
- Observation — a minor gap that doesn’t yet represent a risk but should be monitored.
- Minor nonconformance — a control is documented but not consistently applied.
- Major nonconformance — a control is missing, not functioning, or creating active risk.
Closure verification deserves its own rigor. MOM circulars have flagged cases where auditors failed to validate implementation before signing off on closure, treating a corrective action plan as proof the problem was fixed. Treat every closure claim as a new audit item: ask for photographic evidence, updated logs, or a follow-up interview before you mark anything resolved.
Where ConSASS and ISO 45001 Fit Into Your Audit
ConSASS applies specifically to construction worksites with a contract sum of $30 million or more, and it isn’t optional at that threshold. ConSASS audit scores and supporting documents must go through MOM’s WSH eServices portal, and the standardized scoring format shifts the conversation from subjective impressions to objective maturity levels that regulators can compare across projects.
Below that threshold, aligning your internal audit elements to SS ISO 45001 clauses gives you a defensible structure even without a mandatory ConSASS submission. The clause numbers map cleanly onto audit checklist categories: leadership and worker participation, planning and risk assessment, operational controls, and performance evaluation.
- Confirm your contract sum against the $30 million ConSASS threshold before deciding your audit standard.
- Map your internal checklist elements against SS ISO 45001 clauses even when ConSASS doesn’t apply.
- Keep submission records organized in advance since regular ConSASS reviews reveal maturity gaps months before a formal audit deadline forces the issue.
Where Internal Audits Go Wrong on Real Sites
The single most common failure is auditing the file, not the floor. A binder full of risk assessments tells you nothing about whether the crew on level 12 is actually following the permit conditions written six months ago. Interviews and physical sampling catch what documents hide.
The second failure is treating closure as an administrative step. A supervisor’s signature confirming “action completed” is not evidence; a follow-up photo, updated log entry, or repeat interview is. Draft TAL guidelines on WSHMS implementation reinforce that audits should generate evidence for management action, not simply produce a compliance stamp.
- Sample at least one physical verification per checklist element, not just per audit overall.
- Combine document review with worker interviews so findings reflect what actually happens, not what the paperwork claims.
- Reference real audit examples from comparable projects when calibrating how strict your scoring should be.
Pro Tip: Pick one element per audit cycle and interview five workers instead of one. A single confident answer tells you little; five inconsistent answers tell you the training didn’t stick.
Why We Treat Internal Audits as Foundational, Not Optional
Every serious safety failure we’ve reviewed traces back to a control that existed on paper but never got tested against reality. An internal WSH audit, run properly, is the cheapest insurance a construction project can buy against exactly that gap. It catches drift between what a policy says and what a crew actually does, months before an incident or a regulator forces the comparison.
Readers weighing whether their current audit approach holds up can review case studies and client outcomes on the Mosaic site for a sense of how this plays out on active projects.
— Aman
Get Expert Support for Your Next WSH Audit
Running a defensible internal WSH audit takes trained auditors, a consistent scoring method, and the discipline to verify closure rather than accept a signature. A WSH Audit and Inspection service can address that gap by providing an outside team that walks the floor, tests the three columns, and delivers a report management can act on instead of file away.
If your contract sum puts you into ConSASS territory, or you’re preparing for one, our ConSASS support covers readiness assessment and submission through MOM’s WSH eServices. Smaller projects that want to build internal audit capacity can lean on our training and documentation support instead of a full external engagement. The decision usually comes down to bandwidth: if your team has trained auditors and time to run the process properly, self-audit works. If not, a scoped external audit closes the gap faster than building that capability from scratch. Reach out through our WSH Audit and Inspection page to scope your next audit cycle.
Where to Verify the Rules Yourself
Check MOM’s SHMS requirements for frequency bands, ConSASS submission guidance for construction thresholds, and an EPC assessor selection guide for broader auditor-competence benchmarks.
Sources
FAQ
What Is the Average Salary for an Internal Auditor in Singapore?
Salaries vary widely by industry, seniority, and whether the role sits within a construction firm versus a broader corporate audit function, and no single reliable figure applies across all sectors. Safety-focused internal auditors in construction often hold combined roles (safety officer plus internal auditor), which further affects how compensation gets structured.
What Are the Four Key Aspects of WSH Regulations in Singapore?
WSH regulation in Singapore generally centers on risk management (identifying and controlling hazards), the Safety and Health Management System, workplace safety and health training and competence, and reporting obligations for incidents and audits. Companies over specified contract sum thresholds face additional requirements, including ConSASS submissions for larger construction worksites.
What Are the Requirements for an Audit in Singapore?
Requirements depend on worksite risk profile and contract value. Worksites under $30 million generally need internal reviews at least every six months, while larger construction sites and high-exposure workplaces face mandatory external or third-party audits under programs like ConSASS and MOM’s WHS+ framework.
What Is the “Big 4” in Singapore?
The “Big Four” refers to the major global accounting and professional services firms operating in Singapore, not to workplace safety auditors specifically. WSH audits are a distinct discipline handled by MOM-recognized internal auditors or specialist safety consultancies, not by general accounting firms.
Can I Conduct My Own Internal WSH Audit Without Hiring an External Auditor?
Yes, provided the auditor has completed recognized training such as an ISO 45001 internal audit course and maintains independence from the area being audited. Higher-risk worksites and those crossing the ConSASS contract sum threshold face mandatory external audit requirements regardless of internal capability.